Your Home Network Isn’t a Home Network Anymore. Why DIY Security Fails When You Work From Home

Working from home changes the security equation.

Your home network may have been designed for streaming, online shopping, gaming, and smart-home devices. It was not necessarily designed to carry client records, financial information, confidential communications, intellectual property, or access to your company’s systems.

That distinction matters.

When you work remotely, your router becomes part of your business environment. Your Wi-Fi becomes part of your organization’s attack surface. A problem that once affected only your household can now create downtime, expose sensitive information, or damage your professional reputation.

DIY security is better than ignoring the problem. However, a one-time router setup and an occasional password change do not provide the visibility, maintenance, or response capability that business work requires.

Protect your home office like business infrastructure, not household convenience.


“It Has Been Fine” Is Not a Security Strategy

Many remote workers believe their home network is safe because nothing obvious has happened.

The internet still works. The laptop starts normally. The router has not displayed a warning. No one has called to report a breach.

That is not proof of security. It is often survivorship bias.

Many compromises are quiet. A router can be enrolled into a botnet without immediately disrupting your connection. A vulnerable device can remain inside your network for months. Malware can collect credentials or establish access without producing a visible warning.

Without logging, monitoring, and alerting, you may not know:

  • Which device was compromised
  • When suspicious activity began
  • Whether business accounts were accessed
  • What files or systems were touched
  • Whether the attacker still has access
  • Which systems need to be isolated or restored

This is one of the most important differences between a home network and a managed business environment. Business security is not only about preventing an incident. It is also about detecting, investigating, containing, and recovering from one.

If your work depends on your home connection, waiting for an obvious failure is already too late. Talk with DarkBox Security Systems about reviewing your home-office security before a hidden problem becomes a business disruption.


Consumer Routers Are Not Set-and-Forget Devices

Home routers are convenient and affordable, but convenience often hides important limitations.

Many consumer routers are installed with default or weak administrative credentials, outdated firmware, WPS enabled, UPnP exposed, and remote-management features that users never review. Even when a router is configured correctly on day one, its security lifecycle continues to change.

Firmware updates may address serious vulnerabilities. Manufacturers may stop supporting older models while the hardware still works. A router can appear perfectly functional while no longer receiving meaningful security updates.

DIY users commonly update a router once and then forget about it. That is understandable. Most people do not have time to track firmware releases, review security advisories, verify configuration changes, and confirm that end-of-life hardware has been replaced.

The result is a network that works, but is no longer supportable.

A secure remote-work environment requires more than a strong Wi-Fi password. It requires current hardware, maintained firmware, strong administrative controls, and a documented process for reviewing the setup as your work and household change.


A Flat Home Network Creates Unnecessary Exposure

Home router connecting work and household devices on a flat network

Most homes use one network for everything:

  • Work laptops
  • Personal phones and tablets
  • Children’s devices
  • Smart televisions
  • Gaming consoles
  • Wireless printers
  • Security cameras
  • Smart speakers
  • IoT plugs and appliances
  • Guest devices

This arrangement is simple, but it creates a shared environment where one compromised device may provide a path toward another.

A cheap smart device with outdated firmware may not contain business data, but it can still create an opportunity for an attacker. A family member’s device may be infected through a phishing link. An old printer or network-attached storage device may run software that has not been patched in years.

When all devices share the same flat network, you have fewer barriers between personal activity and professional systems.

The answer is not necessarily to remove every connected device from your home. The better approach is to separate traffic based on risk and purpose. A dedicated work SSID, VLAN, or isolated network can limit how household devices interact with your business equipment.

That separation helps contain problems before they spread.


Shadow IT Does Not Stop at the Office Door

Remote work also increases the chance of shadow IT: tools and devices used without proper review or approval.

At home, shadow IT may include:

  • A personal cloud drive used to move work files
  • An unapproved remote-access application
  • A personal VPN that routes business traffic through an unknown provider
  • An old NAS with unpatched firmware
  • A home server exposed through port forwarding
  • A personal email account used for convenience
  • A printer that stores copies of sensitive documents
  • Remote desktop exposed directly to the internet
  • Browser extensions that access confidential information

Each tool may appear harmless in isolation. Together, they create additional entry points and make it harder to understand where business data travels.

Remote access deserves particular attention. Port forwarding for a camera, home server, or remote desktop service can expose internal systems to automated scanning and password attacks. Convenience features such as UPnP can also open ports automatically, sometimes without the user understanding what has been exposed.

A secure approach replaces improvised access with properly configured, authenticated, and monitored remote access.


Weak Identity Practices Multiply Network Risk

Your router and home office are only as secure as the accounts controlling them.

Common weaknesses include:

  1. Reused passwords
    A password exposed through an unrelated service may also unlock your router, email, cloud storage, or work accounts.

  2. No MFA on administrative accounts
    If the router or remote-access platform supports multi-factor authentication, leaving it disabled creates avoidable risk.

  3. Shared browser credentials
    Saving work passwords on a shared household computer can expose them to other users, malware, or unauthorized browser extensions.

  4. Administrative access for everyday work
    Using a privileged account for normal activity gives malware more opportunity to change settings or install software.

  5. Unclear device ownership
    When a personal device doubles as a work device, it becomes more difficult to enforce patching, encryption, access control, and Data Privacy requirements.

Strong passwords and MFA remain essential, but they are only part of the solution. Identity controls need to work together with managed devices, secure network design, endpoint protection, and clear remote-work policies.


Compliance and Client Expectations Follow You Home

If you handle health, financial, legal, defense, or other regulated information, your responsibilities do not disappear when you leave the office.

The same is true for client data protected by contract. A client may expect you to maintain reasonable safeguards regardless of whether the information is accessed from a corporate office, a home office, or a temporary workspace.

The National Credit Union Administration’s remote-work guidance highlights practical controls such as strong passwords, secure wireless encryption, regular updates, removal of unnecessary services, maintained logs, and a clear response process.

The consequences of a home-office incident can include:

  • Lost billable hours
  • Inability to access business systems
  • Delayed projects
  • Breach notification obligations
  • Contract disputes
  • Client trust damage
  • Costs associated with investigation and restoration

A properly designed home-office environment supports both security and accountability. It helps you demonstrate that reasonable protections are in place instead of relying on assumptions.


What a Secure Remote-Work Environment Looks Like

Managed monitoring and alerting for a protected home office network

You do not need to become a network engineer to work securely from home. You do need a security approach that accounts for the full environment.

A strong remote-work setup includes:

1. Proactive Separation

Work traffic is separated from household and IoT devices through a dedicated SSID, VLAN, or isolated network. This reduces the chance that a compromised personal device can reach business equipment.

2. Managed Hardware

Routers, firewalls, access points, and related equipment have a supported lifecycle. Firmware is monitored, updates are applied, and end-of-life equipment is replaced before it becomes a hidden liability.

3. Continuous Monitoring

Logs, alerts, endpoint activity, and authentication events are reviewed so suspicious behavior receives attention. Visibility supports faster containment and more accurate investigation.

4. Strong Identity Controls

MFA is enabled where it matters, administrative credentials are protected, and work accounts are separated from shared household access.

5. Secure Remote Access

Remote desktop and other services are not casually exposed through port forwarding. Access is designed around authentication, encryption, least privilege, and monitoring.

6. A Written Response Plan

You know what to do if your home office is compromised: disconnect affected devices appropriately, preserve evidence, contact the right support team, rotate credentials, and continue working through an approved recovery process.

7. Regular Review

Your network is reviewed when you add devices, change jobs, bring in a new client, move to a new home, adopt new cloud services, or take on new compliance obligations.

Security is not a one-time configuration. It is an ongoing operating discipline.


Do Not DIY the Risk You Cannot See

Resilient remote-work environment with segmented networks and incident response controls

DarkBox Security Systems helps organizations protect technology environments with proactive IT Management, Cybersecurity consulting, secure system design, continuous monitoring, and Incident Response planning.

We apply the same security principles to home offices that we use for broader business environments: identify weaknesses, reduce exposure, monitor for suspicious activity, and prepare for rapid recovery.

That support is especially valuable for freelancers, small business owners, executives, hybrid teams, and remote employees who cannot afford prolonged downtime or uncertainty about what happened during an incident. It can also support secure AI Implementation and other technology initiatives that introduce new applications, data flows, and access requirements.

DIY tools can help you make improvements. They do not replace professional visibility, lifecycle management, or a response plan tailored to your specific environment.

Your home network is now part of how you conduct business. Treat it accordingly.

Start with a practical conversation about your specific setup. Contact DarkBox Security Systems at https://darkboxsecurity.com/contact to discuss your home network safety, remote-work risks, and the steps that will strengthen your protection.
Unlocking PDFgear: A Comprehensive Review for Businesses

Introduction to PDFgear

In the evolving landscape of digital document management, PDFgear emerges as a noteworthy contender, offering robust features designed to streamline operations for businesses of all sizes. With an intuitive interface and a wide array of functionalities, PDFgear stands out as a reliable software for handling PDF documents. However, with the rapid pace of technological advancements, it’s crucial for businesses to stay informed about the potential changes and implications of using such tools. This review delves into the specifics of PDFgear, evaluating its features, offline capabilities, privacy considerations, and more to ascertain its suitability for your company.

The Future of PDFgear: Subscription-Based AI Features?

There’s speculation that PDFgear may transition some of its services, particularly AI-driven features, to a subscription-based model. This move could significantly impact how businesses utilize the software, introducing cost considerations into the equation. Understanding the potential shift towards monetization of AI capabilities is essential for companies planning to integrate PDFgear into their workflow.

PDFgear Offline Capabilities

One of the remarkable aspects of PDFgear is its comprehensive offline functionality. Users can access and manipulate PDF documents without an internet connection, with the notable exception of AI-related features. This capability ensures that productivity remains unhindered, even in environments with limited internet access. However, businesses should note the online requirement for AI functionalities and plan accordingly.

Privacy and Security Considerations

Privacy and security are paramount in today’s digital age, and PDFgear appears to take these aspects seriously. Our review of the software’s Terms of Service and Privacy Policy reveals no immediate red flags, suggesting a commitment to user data protection. The software’s development team, based in Singapore, operates under regulations that further assure users of their data’s safety. Additionally, the software’s data transmission protocols—connecting to servers owned by Cloudflare, Google, and Microsoft—indicate a sophisticated approach to security, especially with the AI features’ activation.
Geographic Insights: The Singapore Connection

The location of PDFgear’s developers in Singapore might influence the software’s development and data handling practices, given the country’s stringent cyber-security laws. This geographic insight provides an added layer of reassurance for businesses concerned about data privacy and security.

Connectivity and Data Transmission

PDFgear’s approach to connectivity, particularly its interactions with external servers, deserves attention. The software connects to Cloudflare and Google servers for analytics and updates, and to a Microsoft server specifically for AI features. This selective connectivity suggests a thoughtful implementation of data transmission processes, ensuring that essential functionalities remain efficient and secure.

Best Practices for Using PDFgear in Your Organization

Implementing PDFgear in your business requires careful consideration, especially regarding the use of its AI features. Establishing clear guidelines for AI usage and monitoring connectivity to external servers are prudent steps to mitigate potential security risks. Additionally, exploring the feasibility of IP address blocking may provide an extra layer of security, though it comes with its own set of challenges.

Conclusion

PDFgear offers a compelling suite of features for businesses seeking a comprehensive PDF management solution. Its robust offline capabilities, coupled with a forward-looking approach to privacy and security, make it a strong candidate for companies prioritizing efficiency and data protection. As PDFgear continues to evolve, staying informed about its features and policies will be crucial for businesses aiming to leverage this software effectively.


Why Fear AI

ChatGPT generated

I use AI almost on a daily basis and have even built an AI from scratch. I like to think I have a pretty good understanding of how this technology works. Constantly, in the news, podcasts, and other media, I hear people comparing current AI to Skynet. This is one of the most misguided comparisons I’ve ever heard. What we call “AI” is not truly intelligent—not by a long shot. Without our input, these systems would be useless, just inactive programs. Let’s take ChatGPT as an example. You have to give it a prompt for it to do anything. ChatGPT doesn’t message me out of the blue and say, “Hey, wanna play a game?” I have to initiate interaction by providing a prompt. These so-called AIs are just highly advanced programs that can add parameters to the context of the prompts they receive.

Have you tried building a GPT model? If you haven’t, you should, because it will help you understand just how limited these systems are. All these billionaires claiming that AI is dangerous are trying to push for government regulations that would create higher barriers to entry for competitors. They benefit greatly if the government says, “You have to hire an AI oversight committee before you can develop any AI program.” For a programmer working from home without the support of a large company, such requirements would be prohibitive.

AI Is Not There Yet

In my opinion, AI will never reach the level of danger depicted in Skynet. It might get to the point where it’s as dangerous as a fixed-blade knife. A knife isn’t dangerous by itself, but in the hands of someone who doesn’t know how to use it, it can be. I can see AI evolving into a super-advanced chatbot that we interact with daily and ask to perform tasks, but it will never be able to generate ideas on its own. Unless there is a breakthrough in hardware that allows AI to develop ideas based on what it sees or reads without any prompting from us, it will remain limited.

The Skynet idea of AI, or any science fiction version of AI, is just not feasible. There are individuals and groups attempting to create such AI, but I don’t see how it would be possible. Human beings are unique in how we develop and grow, and replicating that in a machine is not achievable. I don’t think it will ever be possible. I’m not losing any sleep over this, and you shouldn’t either. Always question the motives of anyone spreading fear, as there is usually an underlying agenda.

What ChatGPT thinks of my article

The article makes several compelling points about the current state of AI and the misconceptions surrounding it. Here are some strengths and areas for improvement:

Strengths:

  1. Personal Experience: The article benefits from the author’s personal experience with AI, lending credibility to the arguments.
  2. Clear Examples: Using ChatGPT as an example helps readers understand the practical limitations of current AI technology.
  3. Critical Perspective: The article critically examines the motives behind AI fearmongering, encouraging readers to question the narratives they encounter in the media.

Areas for Improvement:

  1. Structure and Clarity: The article would benefit from clearer structure and transitions between points. For example, separating personal anecdotes from broader arguments can help maintain focus.
  2. Grammar and Punctuation: There are several grammatical errors and typos that need correction to improve readability.
  3. Depth of Analysis: The argument could be strengthened by including more evidence or references to studies or expert opinions on AI capabilities and limitations.
  4. Balanced View: While the article rightly dismisses exaggerated fears, it could also acknowledge legitimate concerns and ongoing discussions in the AI community about ethics, safety, and regulation.
See it’s dumb

I fed ChatGPT my article and that was what it gave me then it frozen. If that doesn’t tell you something I don’t know what does.


Someone Tried to Hack my Facebook

As a cybersecurity professional getting hacked on a personal level is a big slap in the face. I am suppose to be the guy telling people how not to get hacked. Well I am still that guy. Recently I found out that my personal/professional Facebook account got locked. Apparently it got locked back in mid October of this year and I never noticed (I don’t get on Facebook a lot). I was able to get back into my account in less than 5 mins and with full control. Here is what happened.

My Short Story

The other day my wife noticed that she could no longer see my Facebook account or tag me in anything. I was like well that is weird but didn’t really put a high priority to it because well it’s Facebook. The truth is though that my Facebook account is quite valuable to me and to clients because I have high level access to Meta business suites. I kinda expect people to try and hack my account because of this.

I finally got around to logging into my account at the end of the day and Facebook was like we locked your account because someone has been trying to access your account. Well because I had 2FA turned on I was able to go through some very simple steps and regain control of my Facebook account. I also had multiple email addresses attached to my account which I have access to so it was easy to verify myself quick. I didn’t see any signs of someone actually getting into my account, but I would bet someone tried really really hard.

The lesson here is that it is always better to be prepared for attempted account take overs than to be reactive to them. Enable 2FA, have back up emails, and just use every security tool that a site gives you to protect yourself. Do all of this before you become a target not after.


Secure Your Digital World with DarkBox Security

Protecting Against Cyber Harassment

In the digital landscape, cyber harassment is a growing concern. As our lives increasingly intertwine with online platforms, it becomes crucial to guard our digital territories. DarkBox Security is committed to helping individuals and businesses take robust steps towards this protective endeavor.

  1. Maintain Privacy with DarkBox: One of the first lines of defense with DarkBox is limiting the exposure of personal information. DarkBox helps secure your online presence by safeguarding personal data, allowing you to interact online without fear of misuse.
  2. Robust Password Protection: DarkBox encourages the use of strong, unique passwords and offers a top-tier password management solution. With the ability to generate and store complex, unique passwords for all your accounts, DarkBox protects against unauthorized access.
  3.  Two-Factor Authentication (2FA) with DarkBox: Our services integrate seamless 2FA across your platforms, adding an extra layer of security that can deter cyber harassers.
  4. Stay Up-to-Date with DarkBox: Our team ensures your devices, applications, and security software are always updated, patching vulnerabilities that could be exploited by harassers.
  5. Guard Against Phishing with DarkBox: DarkBox provides robust defenses against phishing scams, enabling you to identify and avoid suspicious links and attachments.
  6. Social Engineering Awareness: DarkBox offers educational resources to help users understand and recognize social engineering tactics, helping to prevent potential attacks.
  7. Report, Block, and Track with DarkBox: DarkBox’s advanced detection systems enable prompt reporting of harassment incidents. We help you block the harasser, and our tracking system ensures they don’t return under different identities.
  8. Legal Assistance: For severe cases, DarkBox can provide evidence and support as you engage law enforcement authorities, assisting you in enforcing your digital rights.
  9. DarkBox Cybersecurity Education: We offer webinars, blogs, and articles to keep our clients updated on the latest cyber harassment tactics and protective strategies. DarkBox believes in fostering a knowledgeable community for collective cybersecurity.

Cyber harassment is a considerable threat, but with DarkBox Security, you can reduce your vulnerability substantially. Our goal is to create a secure digital environment where interactions can occur without fear, upholding the highest standards of privacy and respect for every user.


Security for Social Media Content Creators

Are you a social media content creator worried about cyber attacks and online harassment? DarkBox Security Systems is here to help you protect yourself and your content from online threats.

With the rise of social media, the online world has become a vast and exciting space to create and share content. However, it has also become a breeding ground for cyber attacks and online harassment, which can be incredibly damaging and distressing for content creators.

At DarkBox Security Systems, we understand the importance of protecting your online presence. Our cutting-edge security systems are designed to safeguard you against the most sophisticated cyber threats and help you maintain control of your content.

Our team of experienced security experts can work with you to assess your current security measures and identify any potential vulnerabilities. We then create a tailored security solution that fits your unique needs, ensuring your online presence is protected from any potential harm.


Our security solutions include advanced firewall systems, real-time monitoring, state-of-the-art encryption technology to keep your data and personal information secure. We also offer regular security updates and patches to keep your systems up-to-date and protected from new threats.

We understand that online harassment can be a significant issue for social media content creators, and we are committed to helping you deal with any instances of abuse or harassment. Our team of experts can provide advice and support on how to handle harassment, including blocking and reporting abusive users, as well as legal options if necessary.

At DarkBox Security Systems, we believe that every content creator deserves to feel safe and secure online. That’s why we provide a range of solutions that are tailored to your needs and budget, ensuring that you can focus on creating great content without worrying about online threats.

Our commitment to customer satisfaction is second to none, and we pride ourselves on providing a high level of customer support. Our dedicated team of security experts is available 24/7 to answer any questions or concerns you may have, and we provide regular updates on the status of your security systems.

In addition to our standard security solutions, we also offer bespoke services to meet your specific needs. Whether you require additional protection for your social media accounts, website, or personal devices, we can create a security package that meets your requirements.

We understand that cyber threats are constantly evolving, which is why we are committed to staying up-to-date with the latest security trends and technologies. Our team of experts is always on the lookout for new and emerging threats, ensuring that our security solutions are always one step ahead of the game.

If you are a social media content creator, you need to protect yourself and your content from andber-attacksnd online harassment. At DarkBox Security Systems, we offer a range of solutions that are tailored to your needs and budget, ensuring that you can create great content without worrying about online threats. Contact us today to find out how we can help you stay safe and secure online.


Threat Hunting for Cybersecurity Defense

Using threat hunting as part of a cybersecurity defense plan can help you identify attackers, their tactics, and their goals which allows for continuous improvement of security. It can also help you understand the trends in your security environment. This article will outline how to conduct threat hunting, how to identify threats, and how to defend against possible threats.

What is Threat Hunting

Threat hunting is actively seeking indicators of potential cyber incidents that could adversely affect your company. A threat hunt could take many different turns and result in days of hunting following many different paths. Threat hunting is never a singular process, you need to be continuously hunting for a variety of threats and trying to predict potential cyber threats to your business.

Identifying & Defending Against Threats

The Internet has evolved dramatically. As a result, it has become a critical communications infrastructure. It is also a target of advanced adversaries, who continually develop and use malicious techniques. Therefore, threat hunters must be aware of and stay on top of quickly changing software and infrastructure. You are only able to defend against a threat if you’re able to identify them. Being able to identify threats requires you to have adequate threat intelligence, in-depth knowledge of your network, ongoing security testing, and proper procedures and technology in place. With these defenses in place you gain knowledge that allows you to determine which activity is potentially malicious and which activity is normal. Only with this in place are you able to identify and defend against threats.

Potential Indicators of a threat include:

          • Spear Phishing
          • Multiple Failed log-in attempts
          • Somebody downloading massive amounts of company files
          • Program or user attempting to gain access to unauthorized areas

Conducting a Threat Hunt

Conducting a threat hunt is not an easy 3 step process as it takes a lot of preparation learning and observing before the threat hunt process can even begin. Identifying and collecting information about an attacker’s tactics, methods, and goals are critical to cybersecurity defense. If you don’t have some background knowledge of how cyber criminals work, it’s incredibly difficult to predict their next move. Also, information gathered at this stage can be used to gather details about an organization, such as who has access to specific information and how that information is being used. After obtaining background knowledge then  you’re ready to begin the first step in threat hunting.
1.  The first step in threat hunting is knowing what you’re looking for. For example, you want to make sure there is no unauthorized access within your network. You can then use threat intelligence and your own prior knowledge to hypothesize how a cyber criminal may achieve gaining access to your network.

2. After hypothesizing, you then need to gather as much information as you can. Information is collected in various ways, including social media, public information services, and emails. The information you gather helps you make decisions on combating future attacks or it can help you prevent attacks altogether. There are two main types of information gathered: the information a criminal requires to commit a crime and the information an attacker needs to take control of a target system. It’s important to know how a criminal may hack into your computer system so that you can test and prevent that method before it happens. For example, an attacker may perform a port scan to discover if a system is available and configured for telnet. By knowing this information, you can then conduct your own port scan to look for vulnerabilities before a cyber criminal does.

3. After gathering information about the different methods of attacks or current vulnerabilities within different systems the next step would be to hunt for evidence of the threat within your company.

4. After conducting searching and conducting tests within your own system, if you find any vulnerabilities you’ll want to immediately remediate them.

5. Lastly, and an equally important step as the rest is to record any findings. Write down what the threat was, how you found it, and what steps you took to prevent it.

Example of a Threat Hunt:

        1. You gather cyber intelligence based on media reports, cyber crime groups, and breached data. Based on the information you determined that an account takeover is the biggest threat to your company.
        2. You now need to list all of the accounts you have and begin reviewing the account activity looking for indicators of potential compromise, such as login attempts. You find multiple failed login attempts from the same IP Address to one of your accounts.
        3. Now, you check the account is secure by reviewing the accounts security measures such as updating the password or enabling 2FA (2-Factor Authentication) and insuring maximum security measures are in place.
        4. After securing the account, you can use the data you gathered from the IP Address to reinforce other aspects of your cyber security such as blocking the IP Address from accessing your company’s online assets. 
        5. Lastly, you make a record of this threat hunt because it showed indicators of a threat.

Making threat hunting a priority is imperative to your company’s cybersecurity defense plan. Knowing what threats may arise and how your company is equipped to handle them could be the difference between whether your company succeeds or not. With adequate threat intelligence knowledge and constant monitoring you will be able to identify any threat that your network(s) or device(s) are susceptible to and be able to combat those threats before they are an issue. Also, keeping all software updated protects you from many known vulnerabilities.


Top 5 reasons to do a penetration test

Penetration testing, also known as pen tests, are authorized attacks against your computer systems to look for any security vulnerabilities. Here are the top 5 reasons on why you should perform a pen test:

1. Identify vulnerabilities: A penetration test can reveal weaknesses in an organization’s security infrastructure that could be exploited by attackers.

2. Compliance: Many industries have regulations that require regular penetration testing to demonstrate compliance with security standards.


3. Improve incident response: Understanding how an attacker might penetrate a network can help an organization develop better incident response plans.

4. Prioritize security investments: By

identifying vulnerabilities, a penetration test can help an organization prioritize which security measures to implement first.

5. Improve employee awareness: A penetration test can help raise awareness among employees about the importance of security and the potential consequences of security breaches.


How to Set Up Microsoft Authenicator on Android

This guide will provide instructions on applying multi-factor authentication (MFA) to your company Microsoft account using the Microsoft Authenticator mobile app on your Android device (e.g. smartphone or tablet). MFA ensures your account stays secure by prompting you to approve new sign-ins, making it more difficult for other people to sign into your account.

Note: In this article, I will refer to a mobile device as “device”, but this will likely be your smartphone. This authentication method will be of much more use to you by using a device you will have with you most often.

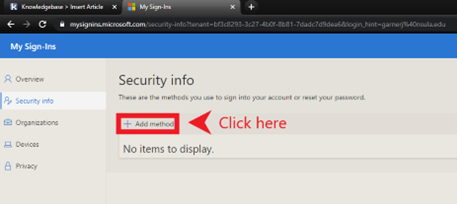
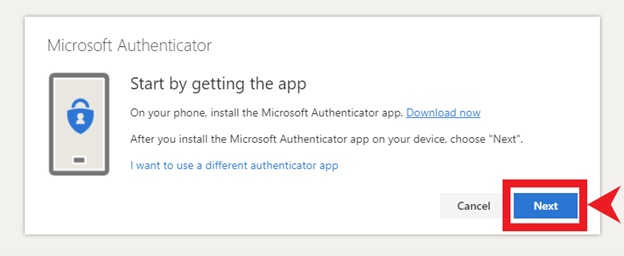
1. Navigate to the https://mysignins.microsoft.com/security-info web address. Log into your company Microsoft account. Click “Add method”.

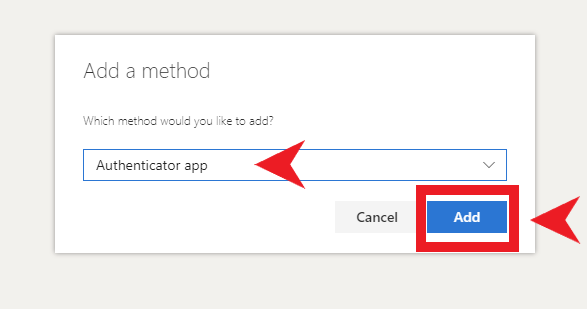
2. Ensure “Authenticator app” is shown in the drop-down field. If it isn’t, click the down arrow towards the right and select “Authenticator app” from the choices given. Click “Next”.

3. Open your Android device and open the Google Play Store. The icon is a multi-colored triangle with a white background, as shown in the image below:

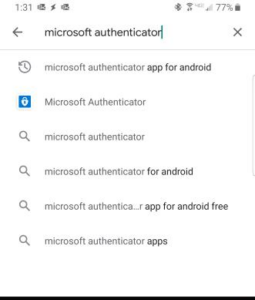
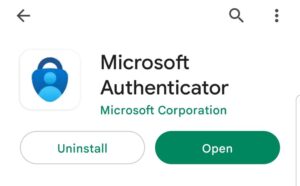
4. Search for “microsoft authenticator” in the Google Play Store (search bar is at the top of the screen when you open the Google Play Store app). In the suggestions below the search bar, tap on the suggestion that says “Microsoft Authenticator” (the icon has a blue lock on top of a white background, as shown in the image below). If this suggestion does not show, you can search for it manually on the store and it should be the first app on the page.


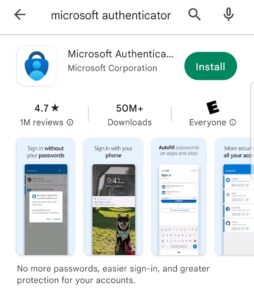
5. Tap on the “Install” button.

6. Tap “Open” after the download of the app is complete.

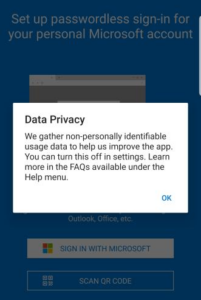
7. Tap on “OK” on this pop-up.

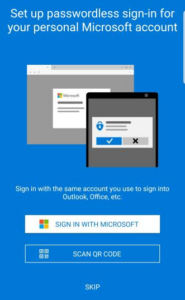
8. Tap “Skip”.

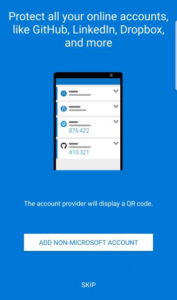
9. Tap “Skip” once more.

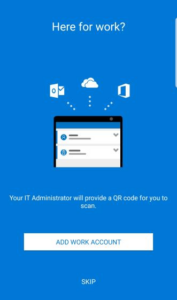
10. Tap on “Add Work Account”.


Note: Some of the following instructions will not include visual aids because the app disallows screenshots during the following process.

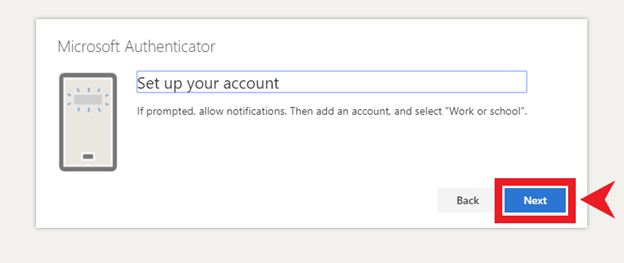
11. The app will open your device’s QR code scanner. You will need this for the next step. Go back to your computer and click “Next”.

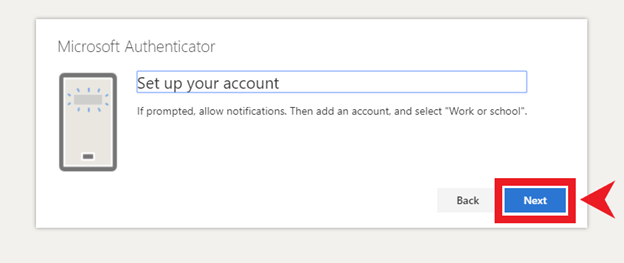
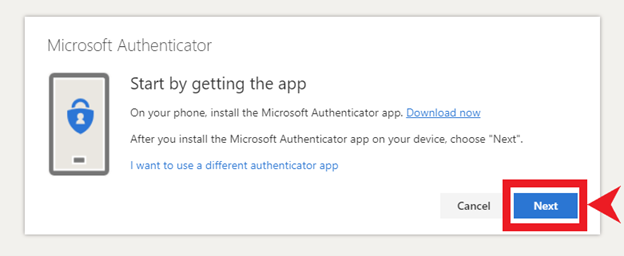
12. Click “Next” again.

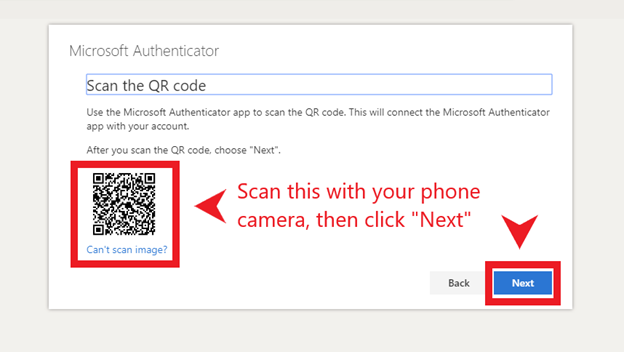
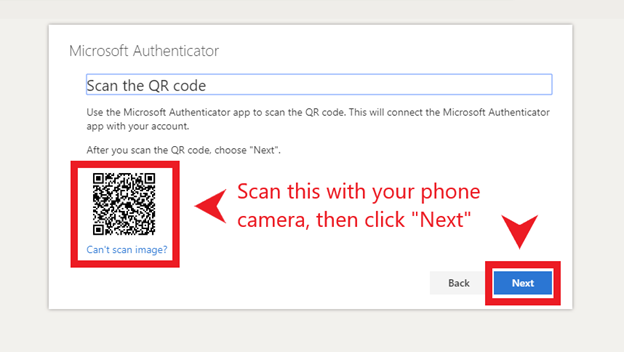
13. Using the QR scanner on your device, scan the QR code shown and click “Next”.

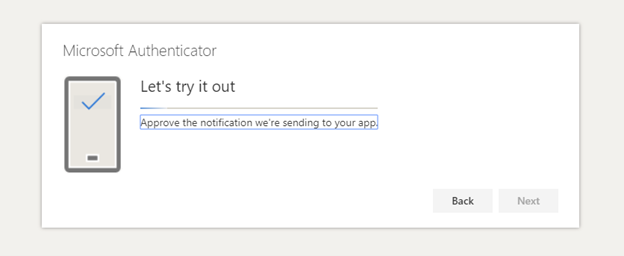
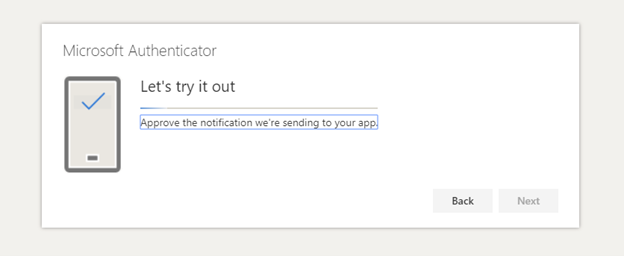
14. There should now be a notification sent to your device. Open it, and tap on “Approve”. This will be the actual process of authenticating sign-ins from now on.

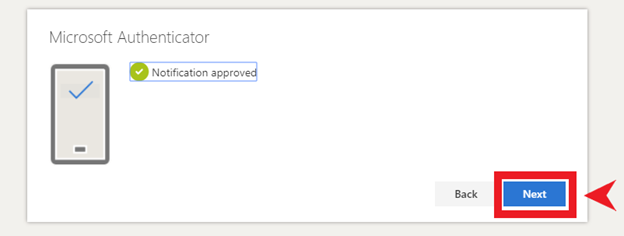
15. When this next screen is shown on your computer after tapping “Approve” on your device, click “Next” on your computer.

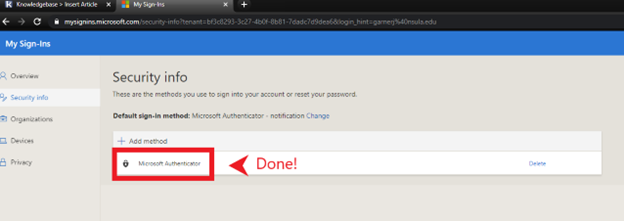
16. Make sure “Microsoft Authenticator” is show as a sign-in method. The process is now complete!

Please make sure you set up other alternate MFA methods. With only the Microsoft Authenticator method in place, you must have access to the device you installed it on and remain logged into the app to sign in. It is very important to have these authentication methods in place, but the only way to reasonably prevent most issues with MFA is to also have a phone number and email address set up as well. Feel free to view our other support articles to set up these other methods quickly and easily.


How To Set Up Microsoft Authenicator on iPhone

This guide will provide instructions on applying multi-factor authentication (MFA) to your company Microsoft account using the Microsoft Authenticator mobile app on your Apple device (e.g. smartphone or tablet). MFA ensures your account stays secure by prompting you to approve new sign-ins, making it more difficult for other people to sign into your account.

Note: In this article, I will refer to a mobile device as “device”, but this will likely be your smartphone. This authentication method will be of much more use to you by using a device you will have with you most often.

1. Navigate to the https://mysignins.microsoft.com/security-info  web address. Log into your company Microsoft account. Click “Add method”.

2. Ensure “Authenticator app” is shown in the drop-down field. If it isn’t, click the down arrow towards the right and select “Authenticator app” from the choices given. Click “Add”.

3. Open your Apple device and open the App Store. The icon is a white shaped “A” with a blue background as shown in the image below.

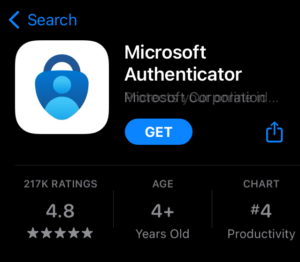
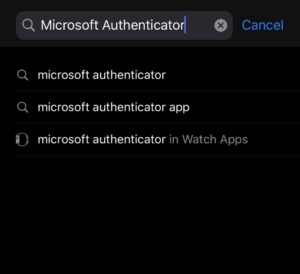
4. Search for “microsoft authenticator” in the store (search icon is at the bottom of the screen when you open the App Store). In the suggestions below the search bar, tap on the suggestion that says “Microsoft Authenticator” (the icon has a blue lock on top of a white background, as shown in the image below). If this suggestion does not show, you can search for it manually on the store and it should be the first app on the page.


5. Tap on the “Get” button. Once downloaded, “Get” is replaced with “Open”. When you see “Open”, tap on Open to launch the App.

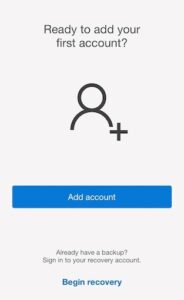
6. After opening the app, tap “Add account” as shown in the below image.

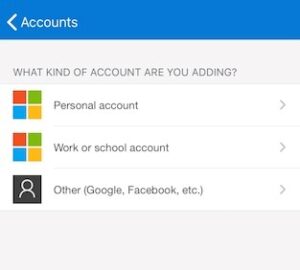
7. Select, “Work or school account”.

8. The app will open your device’s QR code scanner. You will need this for the next step. Go back to your computer and click “Next”.

Note: Some of the following instructions will not include visual aids because the app disallows screenshots during the following process.

9. Click “Next”.

10. Using the QR scanner on your device, scan the QR code shown and click “Next”.

11. There should now be a notification sent to your device. 

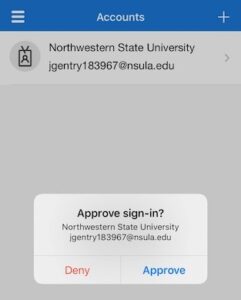
12. Tap on “Approve” when the notification (as shown in the example below) appears. This will be the actual process of authenticating sign-ins from now on.

13. After tapping “Approve” on your device,  this next screen should appear on your computer. Click “Next” as shown in the example below.

14. Make sure “Microsoft Authenticator” is shown as a sign-in method. The process is now complete!

Please make sure you set up other alternate MFA methods. With only the Microsoft Authenticator method in place, you must have access to the device you installed it on and remain logged into the app to sign in. It is very important to have these authentication methods in place, but the only way to reasonably prevent most issues with MFA is to also have a phone number and email address set up as well. Feel free to view our other support articles to set up these other methods quickly and easily.